Analysis
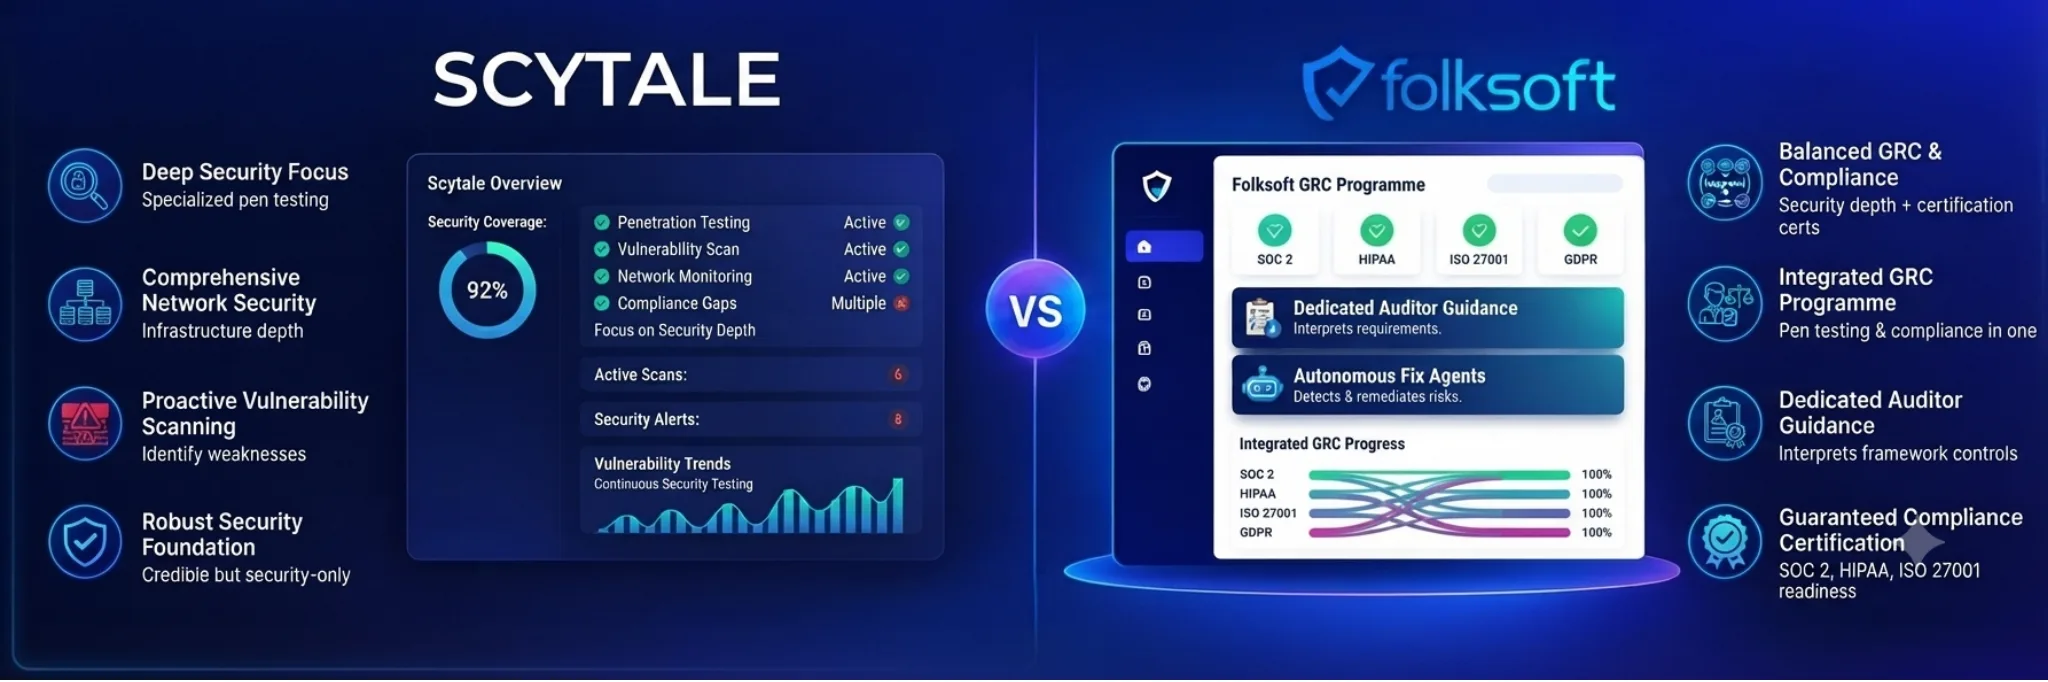
Scytale is startup-built, fast, and genuinely good at what it does — it is the closest platform to Folksoft in the market. The difference is who does the work: Folksoft's autonomous agents remediate findings themselves, and your audit is run by AICPA-accredited independent auditors.
Folksoft is a strong Scytale alternative for startups that want their compliance programme executed, not just guided. Scytale is US-based, purpose-built for startups, and pairs dedicated advisory with compliance automation across SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS — it is well regarded for fast implementation and a high audit pass rate, and it is the closest positioning match to Folksoft in the market. The two overlap heavily, and the differences are narrow but real. Folksoft's autonomous remediation agents apply fixes themselves across AWS, Azure, GCP, GitHub and GitLab rather than advising your engineers on what to change; the audit is performed by AICPA-accredited independent auditors who are not part of the platform vendor, so the relationship stays yours; a dedicated GRC analyst owns policies, evidence, gap tracking and auditor coordination as your compliance function; pricing is transparent flat pricing published from day one; and Folksoft additionally covers ISO 42001, DORA, NIS 2, FERPA, CCPA and 21 CFR Part 11 for AI, fintech, edtech and life-sciences teams. Folksoft can also issue engagement letters to unblock enterprise deals while compliance is still in progress.
Scytale is the closest competitor Folksoft has — same audience, same instinct to put humans next to the automation. Most of the feature list matches. These are the places it genuinely doesn't.
This is the real difference. Scytale's advisors are good, and they will tell your team precisely what to fix — but the fixing lands on your engineers. Folksoft's autonomous agents apply the change themselves: MFA enforcement, logging coverage, access control, encryption settings and configuration drift across AWS, Azure, GCP, GitHub and GitLab. Advice closes a ticket in your backlog. An agent closes the finding.
Folksoft's audits are performed by AICPA-accredited independent audit firms that are not part of the platform vendor. The separation matters to a sceptical enterprise reviewer, and it means the audit relationship survives any change of platform. Scytale coordinates the audit through its own partner network alongside its advisory service — convenient, and one fewer thing to arrange, but the platform and the audit path come from the same vendor.
Both companies put a human next to the software — this is the closest part of the comparison, and Scytale's advisory is a genuine strength. The distinction is scope of ownership: Folksoft's dedicated GRC analyst is your compliance function and owns policies, evidence, gap tracking and auditor coordination outright. An advisor guides the person doing the work; if nobody at your company is that person yet, the work still has nowhere to go.
Scytale does not publish pricing — you book a call and receive a tailored quote shaped by frameworks, headcount and the advisory tier you land on. Folksoft publishes flat pricing you can read before you speak to anyone, with the audit fee shown separately rather than folded into a single bundled number.
On the frameworks most startups start with — SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS — the two are level, and we won't pretend otherwise. Folksoft also runs ISO 42001 for AI governance, DORA and NIS 2 for EU financial and critical-infrastructure exposure, FERPA, CCPA and 21 CFR Part 11 — which matters if you are an AI, edtech or life-sciences company whose next requirement isn't on the standard list.
While compliance is still in progress, Folksoft can issue a formal engagement letter so an enterprise prospect's security review can move forward now rather than waiting for the report. Scytale has no equivalent instrument.
Scytale is known for fast implementation and a high audit pass rate, and it is built for exactly the bootstrapped-to-Series-A companies Folksoft serves. If you want a startup-native platform with strong advisors attached and you have someone in-house to work with them, Scytale is a genuinely good answer and you should take their call. Folksoft is the better fit when there is nobody in-house to advise, when you want the remediation done rather than assigned, or when the audit needs to be visibly independent of the platform.
Every Folksoft engagement includes a named, dedicated GRC analyst assigned to that client. Scytale assigns advisors too — this is the closest the two models get. The difference is whether that person guides the work or owns it.
Review and sign off on policies, answer questions in the risk assessment workshop, and implement the technical controls their DevOps team owns. Everything else is Folksoft.
Scytale gives you startup-literate advisors who know the frameworks well and move quickly — a real strength, and valuable if you have someone in-house to work alongside them. But advice is delivered to a person, and the remediation work still lands on your engineers.
This is the closest comparison in the series, so most rows are a tie. Those are marked as ties.
| Feature | Folksoft | Scytale |
|---|---|---|
| Autonomous remediation agents | YesAgents apply the fix across your cloud and code hosts | NoAdvisors identify and guide; your engineers remediate |
| AICPA-accredited independent auditors | YesIndependent of the platform; the relationship stays yours | Via partner networkAudit coordinated by the vendor alongside its advisory |
| Dedicated human expert per engagement | YesNamed analyst owns the programme outright | Yes — tieDedicated advisor included; guides rather than owns |
| Purpose-built for startups | YesPre-seed to Series A | Yes — tieStartup-native by design; a genuine Scytale strength |
| SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS | YesSOC 2, ISO 27001, HIPAA, GDPR, PCI DSS | Yes — tieAll five covered |
| ISO 42001, DORA, NIS 2, FERPA, CCPA, 21 CFR Part 11 | YesAI, EU financial, edtech and life-sciences frameworks | NoCatalogue centres on the core five |
| Transparent published pricing | YesFlat pricing from day one, audit fee shown separately | NoCustom quote after a sales call |
| Fast implementation | YesAgents shorten the remediation phase | Yes — tieWell regarded for speed and audit pass rate |
| Direct auditor access in platform | YesYour auditor gets read-only access directly | Yes — tieIn-platform audit workflow |
| Penetration testing included | YesPhase 1 full test + Phase 2 re-audit model | Add-onAvailable, priced separately |
| Engagement letters for sales unblocking | Yes | No |
| Compliance CI/CD | YesContinuous drift, fix, validate loop | NoContinuous monitoring with a periodic audit cycle |
Five of twelve rows are ties. Scytale is the closest platform to Folksoft in this series, and a comparison that pretended otherwise would not be worth reading.
Scytale quotes after a sales call, and the advisory tier moves the number, so the licence is the one figure you can’t look up. Add the auditor, the readiness work and your own team’s time to see the real year-one total — then get your price with Folksoft.
Both are startup-built, so this comes down to fit rather than capability. These are the cases where Folksoft is the clearer answer.
Teams with nobody to receive the advice — if there is no security engineer or compliance owner in-house, guidance has nowhere to land. Autonomous agents plus a dedicated analyst close that loop without a hire.
Companies whose buyers scrutinise auditor independence — AICPA-accredited independent audit firms, separate from the platform vendor, and the relationship stays yours if you ever switch.
AI, fintech, edtech and life-sciences startups — ISO 42001, DORA, NIS 2, FERPA and 21 CFR Part 11 sit outside the standard startup five, and you will need them sooner than you think.
Founders who want the number before the sales call — flat published pricing, with the audit fee itemised rather than absorbed into an advisory bundle.
Teams who need to unblock an enterprise deal immediately — engagement letters bridge the gap while compliance runs. Scytale has no equivalent.
Companies that want compliance to stay true between audits — a continuous drift, fix and validate loop rather than monitoring that alerts you and waits.
"We shortlisted two platforms that looked almost identical on paper. What decided it was the demo: one showed us a dashboard of everything we needed to fix, the other showed us the same list already closing itself. With two engineers, that wasn't a close call."
Client quotes are being added as consent is confirmed. Named references available on request during your demo.
What founders ask us when they are evaluating Folksoft and Scytale side by side.
Still have questions?Yes, and the two are genuinely close — both are purpose-built for bootstrapped to Series A startups and both pair human experts with automation across SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS. Folksoft differs in three ways: autonomous agents remediate findings rather than advising your engineers on them, the audit is run by AICPA-accredited independent audit firms separate from the platform, and pricing is published flat rather than quoted after a sales call. If you have an in-house owner to work with advisors, Scytale is a strong choice; if you don't, Folksoft is built for that gap.
Scytale's advisors identify what needs fixing and guide your team through it, which works well when someone in-house can act on that guidance. Folksoft's autonomous agents apply the change themselves across AWS, Azure, GCP, GitHub and GitLab — MFA enforcement, logging coverage, access control, encryption settings and configuration drift. The practical difference for a small engineering team is whether compliance findings become sprint tickets or close without reaching the backlog at all.
Yes. Folksoft engagements are audited by AICPA-accredited independent audit firms that are not part of the platform vendor, and your auditor receives direct read-only access to controls, evidence and documents in app.folksoft.tech. Scytale coordinates the audit through its own partner network alongside its advisory service, which is convenient but means the platform and the audit path come from the same vendor. If you ever move platforms with Folksoft, the audit relationship stays yours.
On the core five — SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS — the two are level. Folksoft additionally runs ISO 42001 for AI management systems, DORA and NIS 2 for EU financial services and critical infrastructure, FERPA for edtech, CCPA, and 21 CFR Part 11 for life sciences. That matters if your next customer or regulator asks for something outside the standard startup set.
Scytale does not publish pricing — you book a call and receive a custom quote shaped by frameworks, headcount and advisory tier. Folksoft publishes transparent flat pricing you can read before speaking to anyone, and shows the audit fee separately rather than folding it into a bundled figure. Use the SOC 2 cost calculator to model the full year-one number including auditor fees and your own team's time.
Scytale is a genuinely good platform and worth your shortlist. It is the stronger fit if you already have a security engineer or compliance owner in-house who wants expert advisors to work alongside rather than someone to take the programme off their hands, if you value a single vendor coordinating both platform and audit, and if your requirements stay within SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS. It is well regarded for fast implementation and a high audit pass rate, and that reputation is earned.
Take both demos — they are close enough to be worth the hour. Then ask each one who closes the findings, and who signs the audit report. Book a free demo and meet the analyst who would run your programme.